Blog
Write-ups of bugs I found, broke, or failed to exploit.
The parts of a KNX product file nobody signed
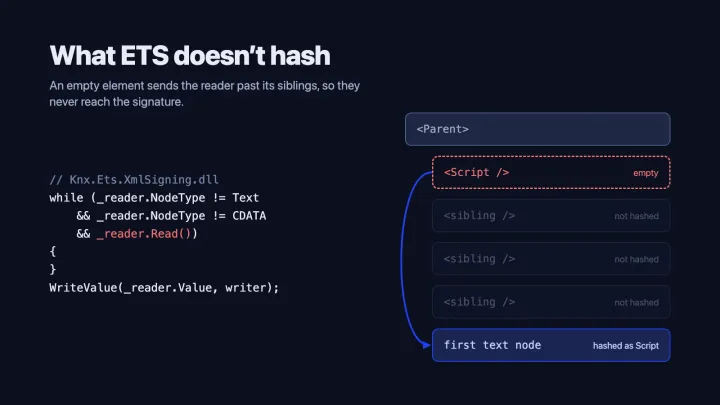
The integrity check ETS runs on KNX product files fails to cover the whole file: a bug in its XML signing library skips elements when it computes the hash, so they may not be protected by the signature at all. I found it while writing my own verifier.
My security cameras text me on Signal
Synology Surveillance Station sees everything my cameras see, but its notifications didn't tell me much. So I built a small service that sends a Signal message, with a snapshot, the moment a camera spots something.
A fragmented MP4 muxer and a sturdier H.264 parser for joy4
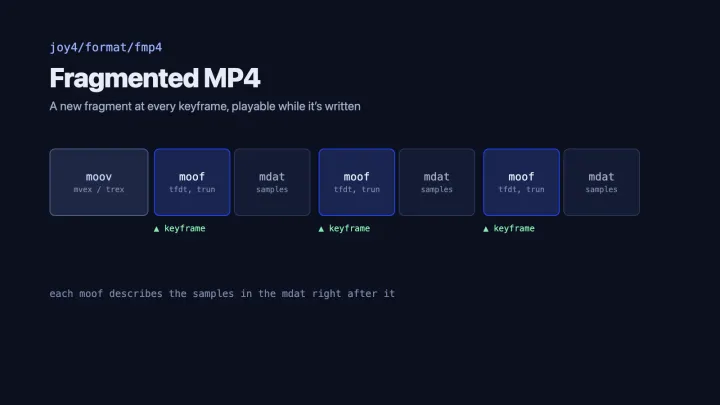
joy4 is a pure Go library for audio and video streams. In my fork I added a fragmented MP4 muxer, so recordings are playable while they're being written, and hardened its H.264 parser with fixes and fuzzing.
HTTP parameter pollution in React Native (<0.69.0)
I investigated the strange quirks of React Native's URL implementation and used them to my advantage.
DoS'ing YouTube with an MP4
I accidentally discovered a potential vulnerability in YouTube during a late-night debugging session on an MP4 muxer. This is the story of how a simple bug in my own code made me rethink the security of a video transcoding pipeline.
Pwning bitcoind RPC to RCE
The bitcoind RPC can be abused to gain remote code execution. Together, the getnewaddress and dumpwallet commands can write files to sensitive locations such as ~/.bashrc or ~/.bash_profile.
Hunting for logic bugs in Monero
How a nested for-loop almost became a money printing press. The story of discovering a bug, and then failing horribly to exploit it.
Private posts
Only you can see these. Prospects see them when their page highlights them.